Free CA1-005 sample questions
Real questions from the SecurityX (Extended) practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 10 of 20 free sample questions.
A security administrator is performing a gap assessment against a specific OS benchmark. The benchmark requires the following configurations be applied to endpoints:• Full disk encryption• Host-based firewall• Time synchronization• Password policies• Application allow listing• Zero Trust application accessWhich of the following solutions best addresses the requirements? (Choose two.)
A global organization is reviewing potential vendors to outsource a critical payroll function. Each vendor's plan includes using local resources in multiple regions to ensure compliance with all regulations. The organization's Chief Information Security Officer is conducting a risk assessment on the potential outsourcing vendors' subprocessors. Which of the following best explains the need for this risk assessment? A.Risk mitigations must be more comprehensive than the existing payroll provider.B.Due care must be exercised during all procurement activities.C.The responsibility of protecting PII remains with the organization.D.Specific regulatory requirements must be met in each jurisdiction.
A manufacturing plant is updating its IT services. During discussions, the senior management team created the following list of considerations:• Staff turnover is high and seasonal.• Extreme conditions often damage endpoints.• Losses from downtime must be minimized.• Regulatory data retention requirements exist.Which of the following best addresses the considerations? A.Establishing further environmental controls to limit equipment damageB.Using a non-persistent virtual desktop interface with thin clientsC.Deploying redundant file servers and configuring database journalingD.Maintaining an inventory of spare endpoints for rapid deployment
A company runs a DAST scan on a web application. The tool outputs the following recommendations:• Use Cookie prefixes.• Content Security Policy - SameSite=strict is not set.Which of the following vulnerabilities has the tool identified? A.RCEB.XSSC.CSRFD.TOCTOU
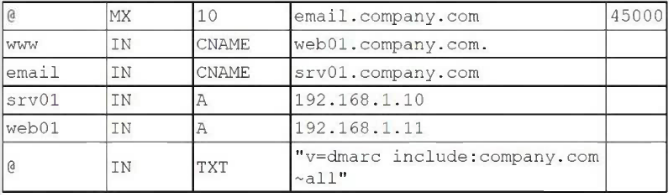
A company hired an email service provider called my-email.com to deliver company emails. The company started having several issues during the migration. A security engineer is troubleshooting and observes the following configuration snippet:Which of the following should the security engineer modify to fix the issue? (Choose two.) A.The email CNAME record must be changed to a type A record pointing to 192.168.1.11B.The TXT record must be changed to "v=dmarc ip4:192.168.1.10 include:my-email.com ~all"C.The srv01 A record must be changed to a type CNAME record pointing to the email serverD.The email CNAME record must be changed to a type A record pointing to 192.168.1.10E.The TXT record must be changed to "v=dkim ip4:192.168.1.11 include :my-email.com ~all"F.The TXT record must be changed to "v=spf ip4:192.168.1.10 include :my-email.com ~all"G.The srv01 A record must be changed to a type CNAME record pointing to the web01 server
A government contractor is preparing for a Cybersecurity Maturity Model Certification (CMMC) Level 2 assessment. The security architect needs to design a solution that enforces data residency for Controlled Unclassified Information (CUI) within a multi-tenant cloud environment, ensuring that data is processed and stored exclusively within U.S. sovereign boundaries. Which cloud architecture and service model would be the MOST appropriate choice to meet this stringent compliance requirement?
A SOC manager is developing a threat hunting program. The initial hunts will be based on Tactics, Techniques, and Procedures (TTPs) from the MITRE ATT&CK framework. The manager wants to create a structured, repeatable process for the hunt team. Which of the following represents the most logical and effective sequence of steps for a hypothesis-driven threat hunt?
A financial institution is deploying a new mobile banking application that will be hosted in a public cloud environment. The security architecture must prevent common web application vulnerabilities, including injection attacks and cross-site scripting (XSS), while also protecting against credential stuffing and application-layer DDoS attacks. The solution must be scalable and managed as a service to reduce operational overhead. Which of the following security services should be placed in front of the application load balancers to meet all these requirements?
A large enterprise is struggling with inconsistent security configurations across its multi-cloud environment, leading to compliance drift and security gaps. The DevSecOps team wants to automate the deployment and validation of security controls to ensure a consistent baseline. Which of the following technologies should be implemented to achieve this goal? (Select TWO).
10 more free samples are waiting
Create a free account to unlock the whole CA1-005 sample bank, or get full access to all 215 practice questions in the simulator.