Free CAS-005 sample questions
Real questions from the SecurityX practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 10 of 20 free sample questions.
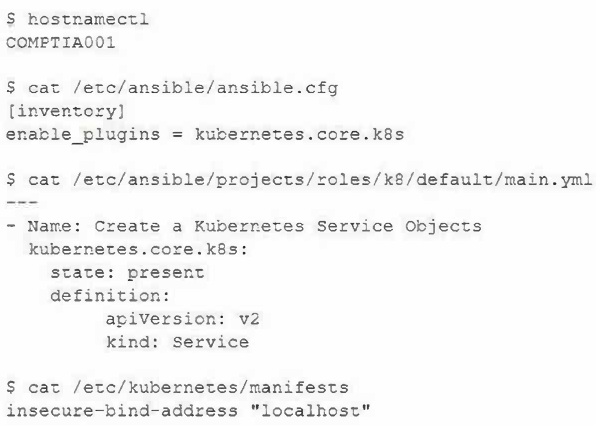
A security architect needs to enable a container orchestrator for DevSecOps and SOAR initiatives. The engineer has discovered that several Ansible YAML files used for the automation of configuration management have the following content:Which of the following should the engineer do to correct the security issues presented within this content?
A CRM company leverages a CSP PaaS service to host and publish Its SaaS product. Recently, a large customer requested that all infrastructure components must meet strict regulatory requirements, including configuration management, patch management, and life-cycle management. Which of the following organizations is responsible for ensuring those regulatory requirements are met?
Company A is merging with Company B. Company A is a small, local company. Company B has a large, global presence. The two companies have a lot of duplication in their IT systems, processes, and procedures. On the new Chief Information Officer's (CIO's) first day, a fire breaks out at Company B's main data center. Which of the following actions should the CIO take first?
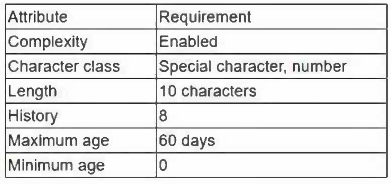
The results of an internal audit indicate several employees reused passwords that were previously included in a published list of compromised passwords.The company has the following employee password policy:Which of the following should be implemented to best address the password reuse issue? (Choose two.)
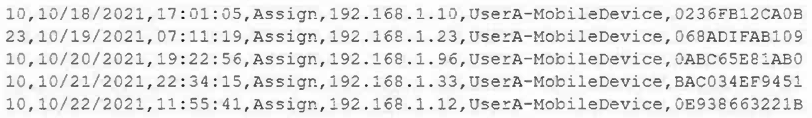
A mobile administrator is reviewing the following mobile device DHCP logs to ensure the proper mobile settings are applied to managed devices:Which of the following mobile configuration settings is the mobile administrator verifying? A.Service set identifier authenticationB.Wireless network auto joiningC.802.1X with mutual authenticationD.Association MAC address randomization
A security analyst is investigating a possible insider threat incident that involves the use of an unauthorized USB from a shared account to exfiltrate data. The event did not create an alert. The analyst has confirmed the USB hardware ID is not on the device allow list, but has not yet confirmed the owner of the USB device. Which of the following actions should the analyst take next?
Which of the following security features do email signatures provide?
A financial services firm is architecting a new cloud-native trading platform using microservices deployed on Kubernetes. To comply with Zero Trust principles, the Chief Architect mandates that service-to-service communication must be authenticated using short-lived, cryptographically verifiable identities, without relying on static secrets like API keys stored in environment variables. The solution must automatically issue and rotate these identities for all workloads. Which of the following technologies should be implemented to meet these requirements?
A security engineer is tasked with creating a SOAR playbook to automate the initial response to a suspected phishing email reported by an employee. The goal is to enrich the indicators of compromise (IOCs) from the email and take initial containment actions without human intervention. Which THREE of the following actions should be included in the automated playbook? (Select THREE)
10 more free samples are waiting
Create a free account to unlock the whole CAS-005 sample bank, or get full access to all 210 practice questions in the simulator.