Free CV0-004 sample questions
Real questions from the Comptia Cloud+ practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 10 of 20 free sample questions.
A company just learned that the data in its object storage was accessed by an unauthorized party. Which of the following should the company have done to make the data unusable? A.The company should have switched from object storage to file storage.B.The company should have hashed the data.C.The company should have changed the file access permissions.D.The company should have encrypted the data at rest.
A customer relationship management application, which is hosted in a public cloud IaaS network, is vulnerable to a remote command execution vulnerability. Which of the following is the best solution for the security engineer to implement to prevent the application from being exploited by basic attacks?
Which of the following is a difference between a SAN and a NAS?
A cloud engineer is troubleshooting an application that consumes multiple third-party REST APIs. The application is randomly experiencing high latency. Which of the following would best help determine the source of the latency?
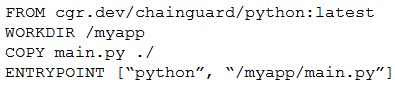
A cloud engineer is reviewing the following Dockerfile to deploy a Python web application:Which of the following changes should the engineer make to the file to improve container security? A.Add the instruction USER nonroot.B.Change the version from latest to 3.11.C.Remove the ENTRYPOINT instruction.D.Ensure myapp/main/py is owned by root.
A financial services company is deploying a new containerized application to an Amazon EKS cluster. A recent security audit mandates that all container images must be scanned for vulnerabilities before being admitted to the cluster, and deployments with 'CRITICAL' severity vulnerabilities must be blocked. Which combination of tools and configurations BEST enforces this policy in an automated fashion?
A lead SRE is designing a monitoring strategy for a distributed application that spans multiple geographic regions and cloud providers. The primary goal is to gain deep insights into request flows and pinpoint performance bottlenecks across service boundaries. Which observability practice is MOST critical to achieving this goal?
A cloud administrator is tasked with implementing a cost-effective backup solution for a 10TB file server hosted on an EC2 instance. The recovery time objective (RTO) is 8 hours, and the recovery point objective (RPO) is 24 hours. Data must be retained for 7 years for compliance. Which AWS service combination meets these requirements MOST efficiently?
A security architect is designing an authentication and authorization system for a multi-cloud environment consisting of AWS and Azure. The requirements are to use the company's on-premises Active Directory as the single source of truth for user identities and to enforce role-based access control (RBAC) consistently across both cloud platforms. Which TWO of the following should be implemented? (Select TWO)
10 more free samples are waiting
Create a free account to unlock the whole CV0-004 sample bank, or get full access to all 226 practice questions in the simulator.