Free 70-744 sample questions
Real questions from the Securing Windows Server 2016 practice bank, with the correct answer and an explanation for each one. No junk, no filler.
Try them in the simulator Same questions, with study, timed and flashcard modes.
Showing 10 of 20 free sample questions.
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contain an Active Directory domain named contoso.com. The domain contains a computer named Computer1 that runs Windows 10. Computer1 connects to a home network and a corporate network.The corporate network uses the 172.16.0.0/24 address space internally.Computer1 runs an application named App1 that listens to port 8080.You need to prevent connections to App1 when Computer1 is connected to the home network.Solution: From Group Policy Management, you create an AppLocker rule.Does this meet the goal? A.YesB.No
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contain an Active Directory domain named contoso.com. The domain contains a computer named Computer1 that runs Windows 10. Computer1 connects to a home network and a corporate network.The corporate network uses the 172.16.0.0/24 address space internally.Computer1 runs an application named App1 that listens to port 8080.You need to prevent connections to App1 when Computer1 is connected to the home network.Solution: From Group Policy Management, you create software restriction policy.Does this meet the goal? A.YesB.No
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contain an Active Directory domain named contoso.com. The domain contains a computer named Computer1 that runs Windows 10. Computer1 connects to a home network and a corporate network.The corporate network uses the 172.16.0.0/24 address space internally.Computer1 runs an application named App1 that listens to port 8080.You need to prevent connections to App1 when Computer1 is connected to the home network.Solution: From Windows Firewall in the Control Panel, you add an application and allow the application to communicate through the firewall on a Private network.Does this meet the goal? A.YesB.No
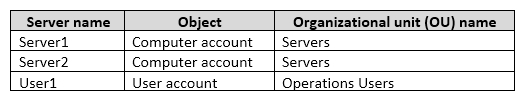
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2016. All client computers run Windows 10.The relevant objects in the domain are configured as shown in the following table.You need to assign User1 the right to restore files and folders on Server1 and Server2.Solution: You create a Group Policy object (GPO), you link the GPO to the Servers OU, and then you modify the Users Rights Assignment in the GPO.Does this meet the goal? A.YesB.No
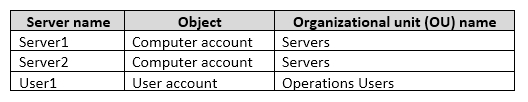
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2016. All client computers run Windows 10.The relevant objects in the domain are configured as shown in the following table.You need to assign User1 the right to restore files and folders on Server1 and Server2.Solution: You add User1 to the Backup Operators group in contoso.com.Does this meet the goal? A.YesB.No
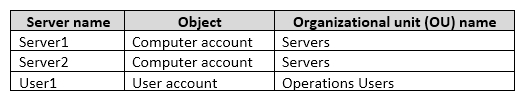
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2016. All client computers run Windows 10.The relevant objects in the domain are configured as shown in the following table.You need to assign User1 the right to restore files and folders on Server1 and Server2.Solution: You create a Group Policy object (GPO), link it to the Operations Users OU, and modify the Users Rights Assignment in the GPO.Does this meet the goal? A.YesB.No
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.After you answer a question in this sections, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.Your network contains an Active Directory domain named contoso.com. The domain contains multiple Hyper-V hosts.You need to deploy several critical line-of-business applications to the network to meet the following requirements:✑ The resources of the applications must be isolated from the physical host.✑ Each application must be prevented from accessing the resources of the other applications.✑ The configurations of the applications must be accessible only from the operating system that hosts the application.Solution: You deploy a separate Windows container for each application.Does this meet the goal? A.YesB.No
A financial institution is deploying a new Active Directory administrative forest based on the Enhanced Security Administrative Environment (ESAE) model. To manage the production forest, administrators will use Privileged Access Workstations (PAWs). A critical security requirement is to prevent any credential theft from RDP sessions initiated from the PAWs to production servers. Which Group Policy setting must be configured and enforced on the production servers to meet this requirement?
A security administrator has implemented a Just-Enough-Administration (JEA) endpoint on a member server to allow junior operators to restart specific services. After deployment, operators report that they can connect to the JEA endpoint but receive an error when trying to run `Restart-Service`. The administrator has verified the Role Capability file (`.psrc`) correctly lists `Restart-Service` in the `VisibleCmdlets` section. What is the most likely cause of this issue?
10 more free samples are waiting
Create a free account to unlock the whole 70-744 sample bank, or get full access to all 162 practice questions in the simulator.